Compliance Engineering
Control mapping, ownership models, implementation support and evidence design.
SERVICES
We help regulated and technology-driven organizations translate complex cybersecurity requirements into practical controls, accountable ownership and defensible evidence.
EU Regulatory ExpertiseNIS2, EUCC, CRA & EU AI Act
Compliance EngineeredRequirements translated into controls
Audit-Ready EvidenceEvidence structured for audit and assurance
Direct, practical supportHands-on help with preparation and implementation
OUR SERVICES
Cybersecurity, governance and assurance services designed to turn complex requirements into practical, resilient operations.
Control mapping, ownership models, implementation support and evidence design.
Applicability analysis, gap assessment and implementation roadmap.
Readiness assessment, control evidence and audit preparation.
Risk assessment, treatment planning and resilience improvement.
Policies, operating models, roadmaps, KPIs and board-level reporting.
Security leadership, program oversight and executive advisory.
Privacy governance, accountability and GDPR-aligned processes.
AI governance, risk classification, controls and responsible-AI oversight.
FLAGSHIP PROGRAMS
Structured implementation support for NIS2, EUCC and CRA — from scope and gap analysis to controls, evidence and readiness.
NIS2
Build NIS2 readiness with clear scope, accountable ownership, implemented controls and evidence.
EUCC
Prepare ICT products for EUCC evaluation with structured requirements, evidence and assurance support.
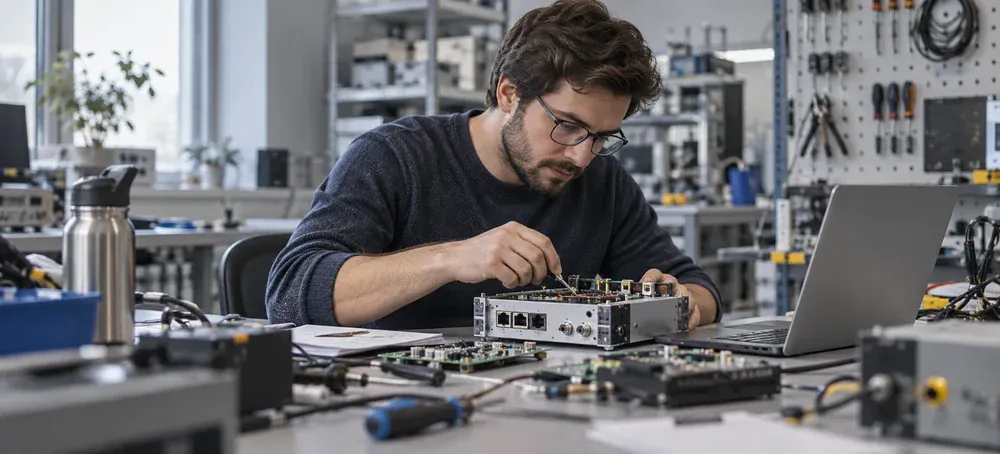
CRA
Embed CRA requirements into product security, vulnerability management and technical documentation.
HOW WE WORK
A structured delivery model that turns regulatory and assurance requirements into implemented controls, accountable ownership and defensible evidence.
Establish scope, obligations and gaps.
Understand business context, applicable requirements, current controls, risks and evidence gaps.
Translate requirements into controls, ownership and evidence.
Define dependencies, priorities and a practical implementation roadmap.
Operationalize controls and build evidence as you go.
Put governance, processes and technical measures into operation with clear accountability.
Validate effectiveness, evidence and readiness.
Review control performance and audit readiness, then improve continuously.
FRAMEWORKS & ASSURANCE
Practical implementation support across European cybersecurity regulation, product assurance, certification and security management.
EU Directive
Critical-entity cybersecurity and resilience.
EU Certification Scheme
European cybersecurity certification readiness.
EU Regulation
Product cybersecurity and lifecycle obligations.
Security Management
Information security management and certification readiness.
Assurance
Controls, evidence and customer assurance readiness.
EU Regulation
AI governance, risk classification and regulatory readiness.
Also supported: GDPR · ISO 27701 · related privacy and assurance requirements
WHO WE SERVE
Cybersecurity, compliance and assurance for essential, regulated and technology-driven organizations across Europe.
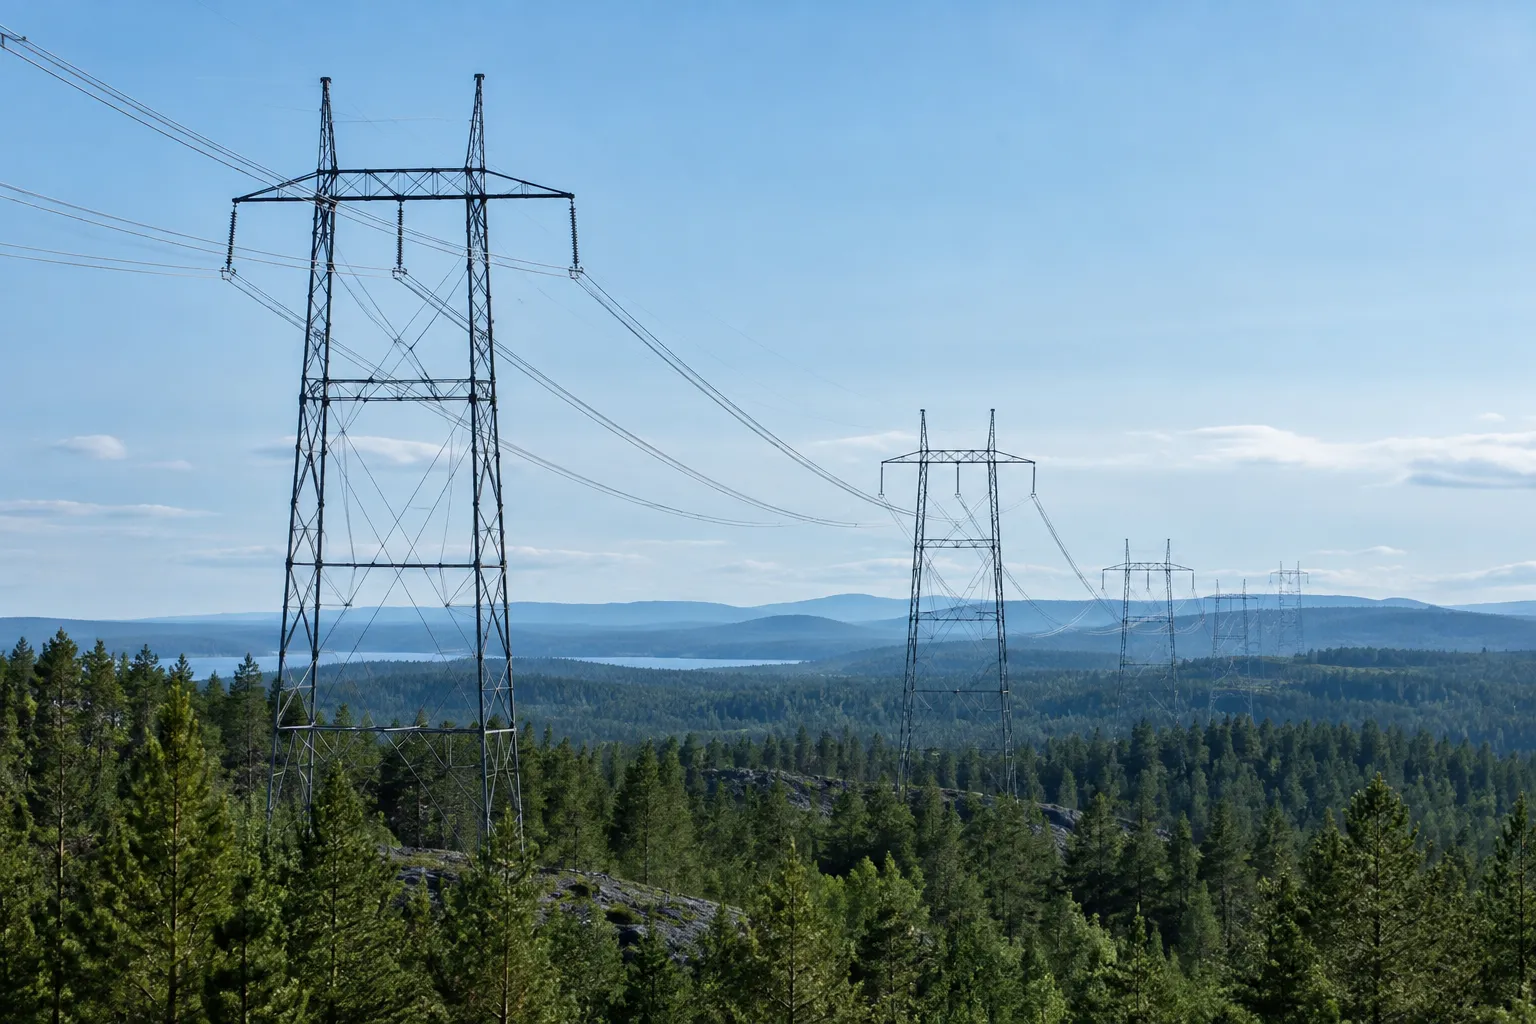
ENERGY
NIS2-aligned governance, cyber risk and operational resilience for energy and utility operators.
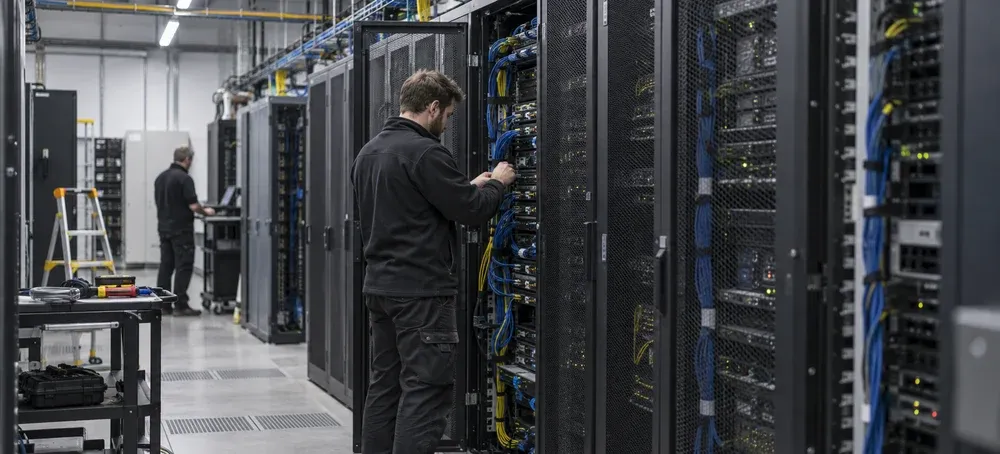
DIGITAL INFRASTRUCTURE
Security, resilience and assurance for data centres, hosting, cloud and digital infrastructure providers.
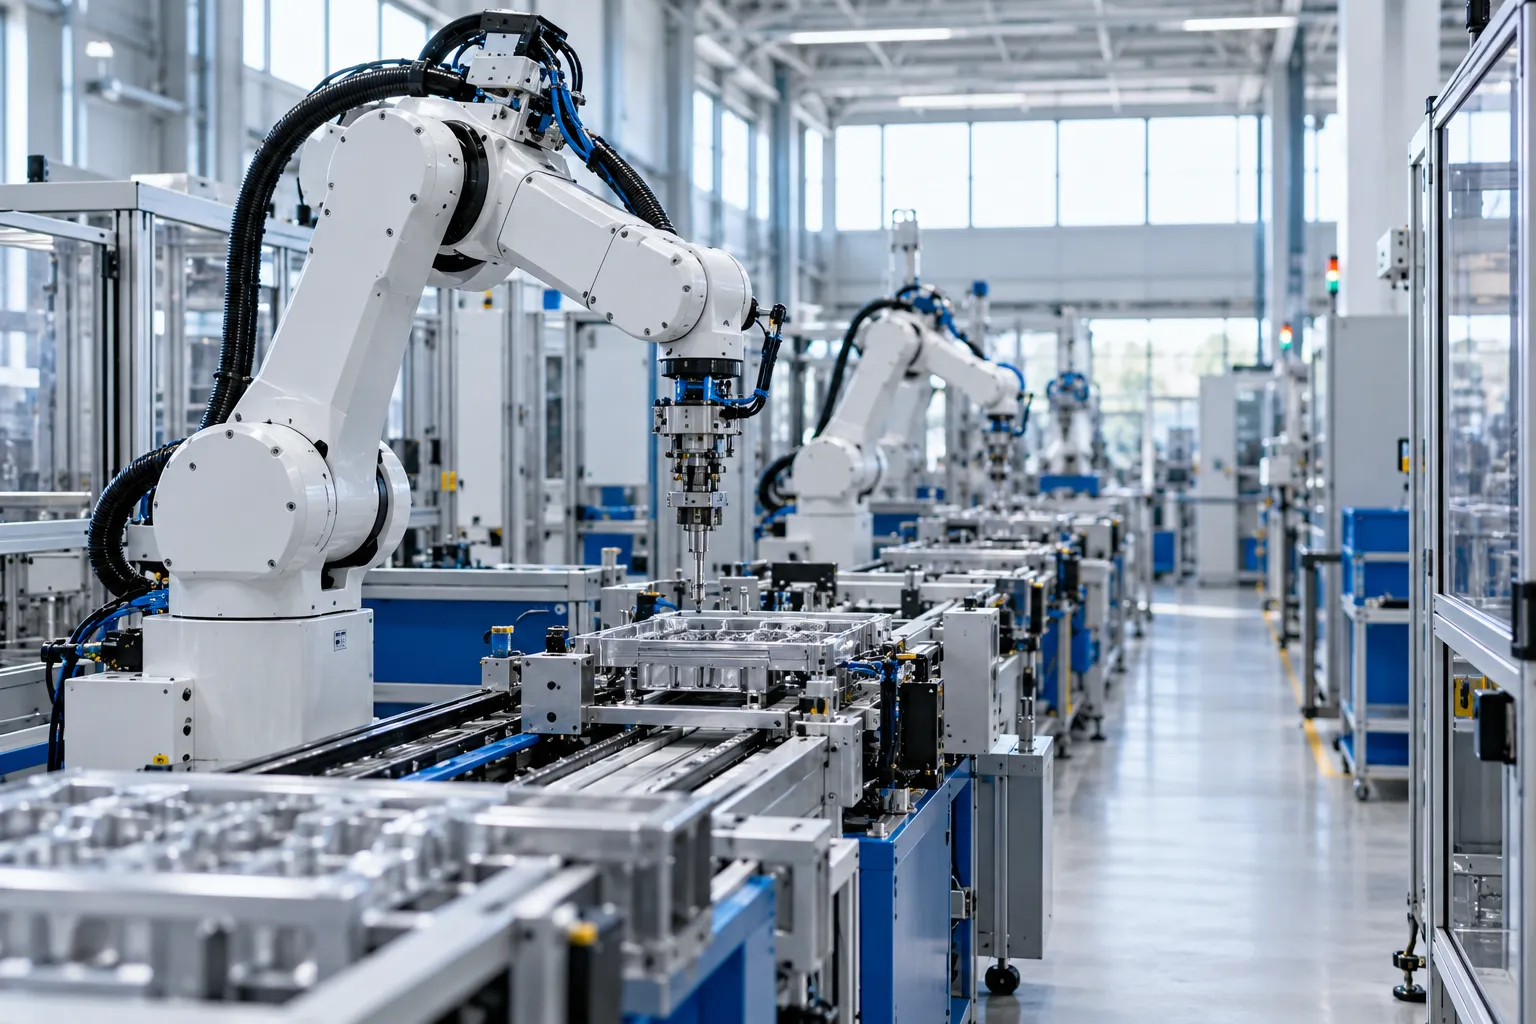
INDUSTRY
Protect connected production, industrial environments, product security and supply chains.
TECHNOLOGY
Build customer trust and enterprise assurance with secure products, ISO 27001 and SOC 2 Type II readiness.
HEALTHCARE
Protect sensitive data, critical digital services and continuity of care.
PUBLIC SECTOR
Strengthen governance, procurement assurance, resilience and regulatory readiness.
START A CONVERSATION
Get expert guidance on NIS2, EUCC, CRA, ISO 27001, SOC 2 Type II and AI governance — from readiness and control design to implementation and assurance.